A promising enterprise deal reaches the final procurement stage. Your customer likes the product, the pricing is agreed upon, and implementation discussions are underway. Then a security questionnaire lands in your inbox. The buyer asks for evidence of SOC 2 or ISO 27001 compliance.
Which security project deserves attention first can come down to that request, for an Australian software company entering enterprise markets. Choosing incorrectly may mean spending months preparing evidence that doesn’t satisfy the customer’s requirements.
Treat a security questionnaire as a prompt to plan rather than something to scramble over. Once you know what the customer actually needs, and the deadline, the options narrow quickly.
Start With the Customer’s Actual Requirement
The SOC 2 vs ISO 27001 decision shouldn’t start with the framework that looks easier to achieve. Start by reading the customer’s contract or security requirements. Where Australian and European enterprise buyers commonly recognize ISO 27001, North American SaaS customers frequently ask for SOC 2 reports.
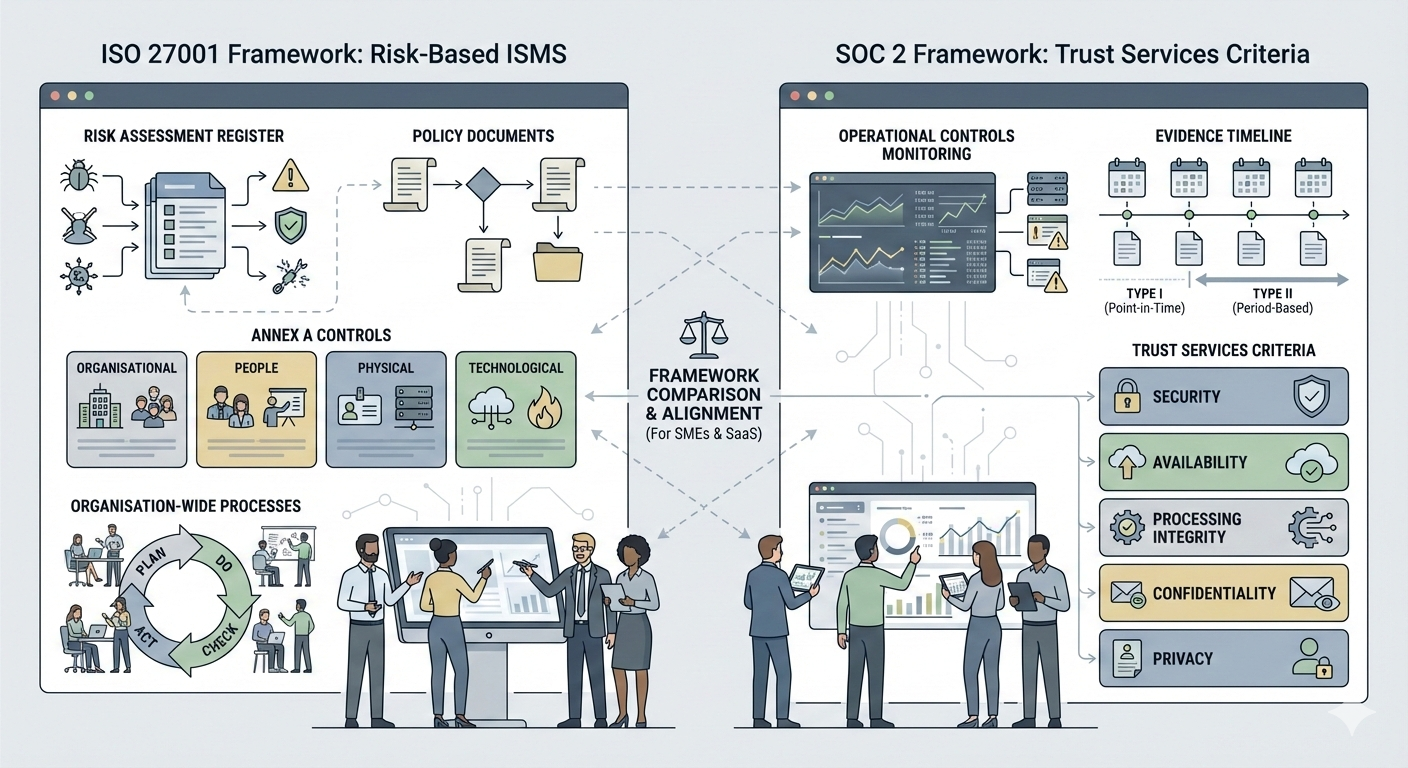
These preferences aren’t universal. Certain customers are happy with either framework, but others specify one. When a contract explicitly requires SOC 2, you can’t assume an ISO 27001 certificate will be accepted instead. Ask the buyer whether equivalent assurance will satisfy the requirement before committing resources.
Two Different Outcomes: Certification and Attestation
What your business receives after the independent assessment is one important distinction in the ISO 27001 vs SOC 2 comparison. Information security management systems are covered by ISO 27001, an internationally recognized standard. An accredited certification body assesses the organization and can issue a certificate that is valid for three years, subject to ongoing surveillance audits. SOC 2 isn’t the same.
Controls are examined against the AICPA Trust Services Criteria by a licensed CPA firm, which issues an attestation report. Controls at a particular point in time are what a SOC 2 Type 1 report evaluates. Their operating effectiveness over a defined period is also assessed in Type 2. There is no formal SOC 2 certification. An auditor’s report, rather than an ISO-style certificate, is what customers see.
The difference matters when you describe your status to customers. Because procurement teams tend to notice the wording, be precise about whether you hold a certificate or a report.
Doing Both Doesn’t Mean Duplicating Everything
The SOC2 vs ISO 27001 discussion often overlooks how much operational work the frameworks share. Security practices such as access management, risk assessment, incident response, supplier oversight, and change management feature in both.
Take a SaaS company that already maintains employee access records, documents security incidents, and reviews important suppliers. Much of that evidence could serve both assessments, even though the requirements and testing methods are different. Organizations that plan to pursue both frameworks can map shared controls early, rather than maintaining completely separate evidence collections.
For many businesses, starting with an ISO 27001 information security management system provides a useful foundation for SOC 2 preparation later on.
Each control should be checked, all the same, against the criteria of the framework in question.
Plan for the Time Behind the Audit
Writing policies isn’t all there is to audit readiness. You need to implement security controls, assign responsibilities, and collect evidence. Australian businesses can get structured compliance support from Siege Cyber, whose programs are designed to achieve audit readiness in approximately three to nine months.
With SOC 2 Type 2, the independent auditor may need an additional observation period before issuing the report. The duration depends on the scope, existing controls, and evidence requirements. Don’t forget to include independent certification and attestation fees in the budget.
There’s an internal cost too, as staff will spend time gathering evidence and answering auditor questions. Settling the scope early, including which systems and services are covered, helps keep the timeline and the budget realistic.
Get More From Compliance Than a Passed Questionnaire
Rather than merely satisfying a customer questionnaire, a well-designed compliance program should improve security operations. Regular access reviews, incident response exercises, employee training, and technical testing can help organizations identify weaknesses and manage risks more consistently.
Siege Cyber provides fixed-price compliance support, Australian-based specialists, and penetration testing within its compliance packages.
Businesses comparing ISO 27001 SOC 2 requirements can draw on this support when assessing existing controls, identifying gaps, and preparing for independent assessment.
The Right Framework Supports Your Next Move
When your immediate opportunity requires SOC 2, make that requirement the priority. ISO 27001 may be the more practical starting point if your customers mainly operate in Australia or Europe. If both markets matter to you, a coordinated approach can cut down on duplicated preparation.
Confirm what your customers will accept, define the systems covered by the assessment, and understand the complete timeline and cost before investing. The right framework meets your business obligations and helps establish security practices your team can maintain.